PHP flaw took 32 UK services offline, but confirmed damage remains unclear
Ministers reported 32 government services unavailable and four partly unavailable amid a PHP flaw. No 10 said major public-facing critical systems were unaff...

A PHP security flaw prompted precautionary outages across UK government services, with ministers reporting 32 unavailable and four partially unavailable. The reports do not establish that attackers exploited the vulnerability or identify which services were affected.
The National Cyber Security Centre said the flaw could, under certain conditions, allow unauthenticated remote code execution on a web server running PHP. It said the issue had been fixed and urged UK organisations to take immediate action. The reports attributed most of the service disruption to precautionary measures as fixes were applied.
A No 10 spokeswoman said no major public-facing critical systems had been affected. The Office for Budget Responsibility website was reported to have been affected, but a cabinet minister said the Budget had not been compromised.
Those statements describe different things: the reported unavailability of services, the potential consequences of the flaw, and the government’s account of which critical systems were affected. A vulnerability that can permit remote code execution is a serious security risk, but that capability alone does not show that anyone used it against government systems.
The available reports do not name the 32 unavailable services or the four partly unavailable ones. They also do not say how long the outages lasted, whether the flaw was exploited, or exactly when the services were taken offline. Without those details, the scale of the precautionary disruption is clearer than any confirmed damage.
The NCSC’s warning was directed at UK organisations more broadly, not only government departments. The episode shows how a flaw in widely used software can lead services to be taken offline while organisations assess and address risk, even when officials say major public-facing critical systems were not affected.
Sources
Editor & Founder
Peter OlaleruPeter is the founder and editor of Measured Take and a cybersecurity professional. He leads our news, fact checks, sport and guides from around the world, with a particular eye on cyber attacks, data breaches, scams, AI and misinformation.
More from Politics
October 22, 2026
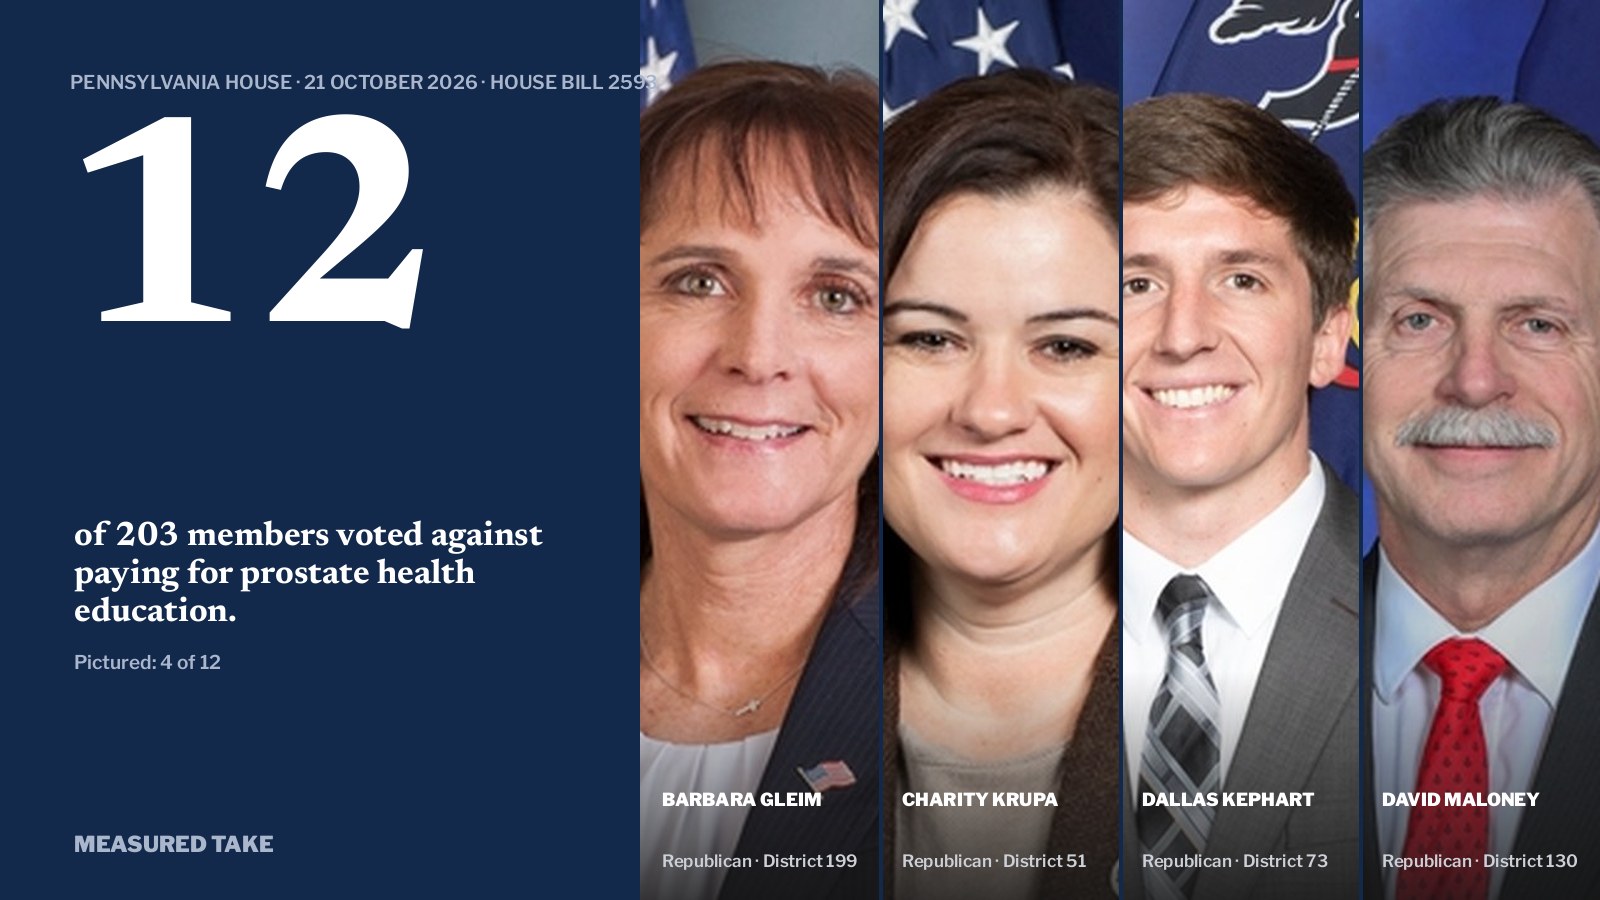
Pennsylvania House backs prostate health education campaign, 191–12
October 22, 2026
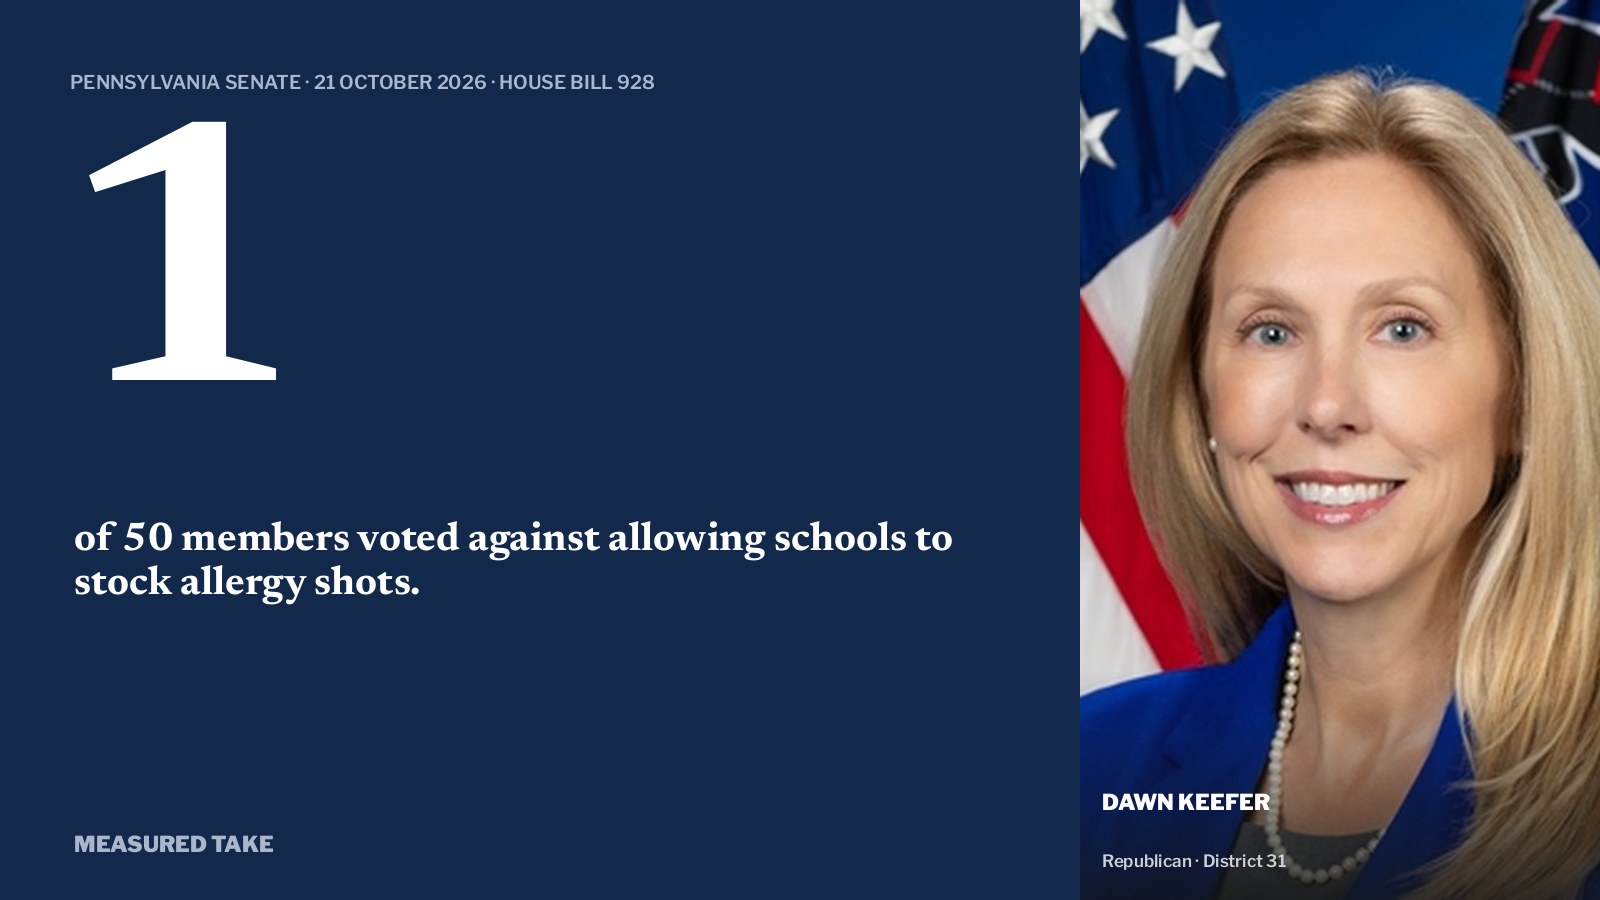
Pennsylvania Senate passes epinephrine auto-injector bill 49–1; Dawn Keefer votes no
October 22, 2026
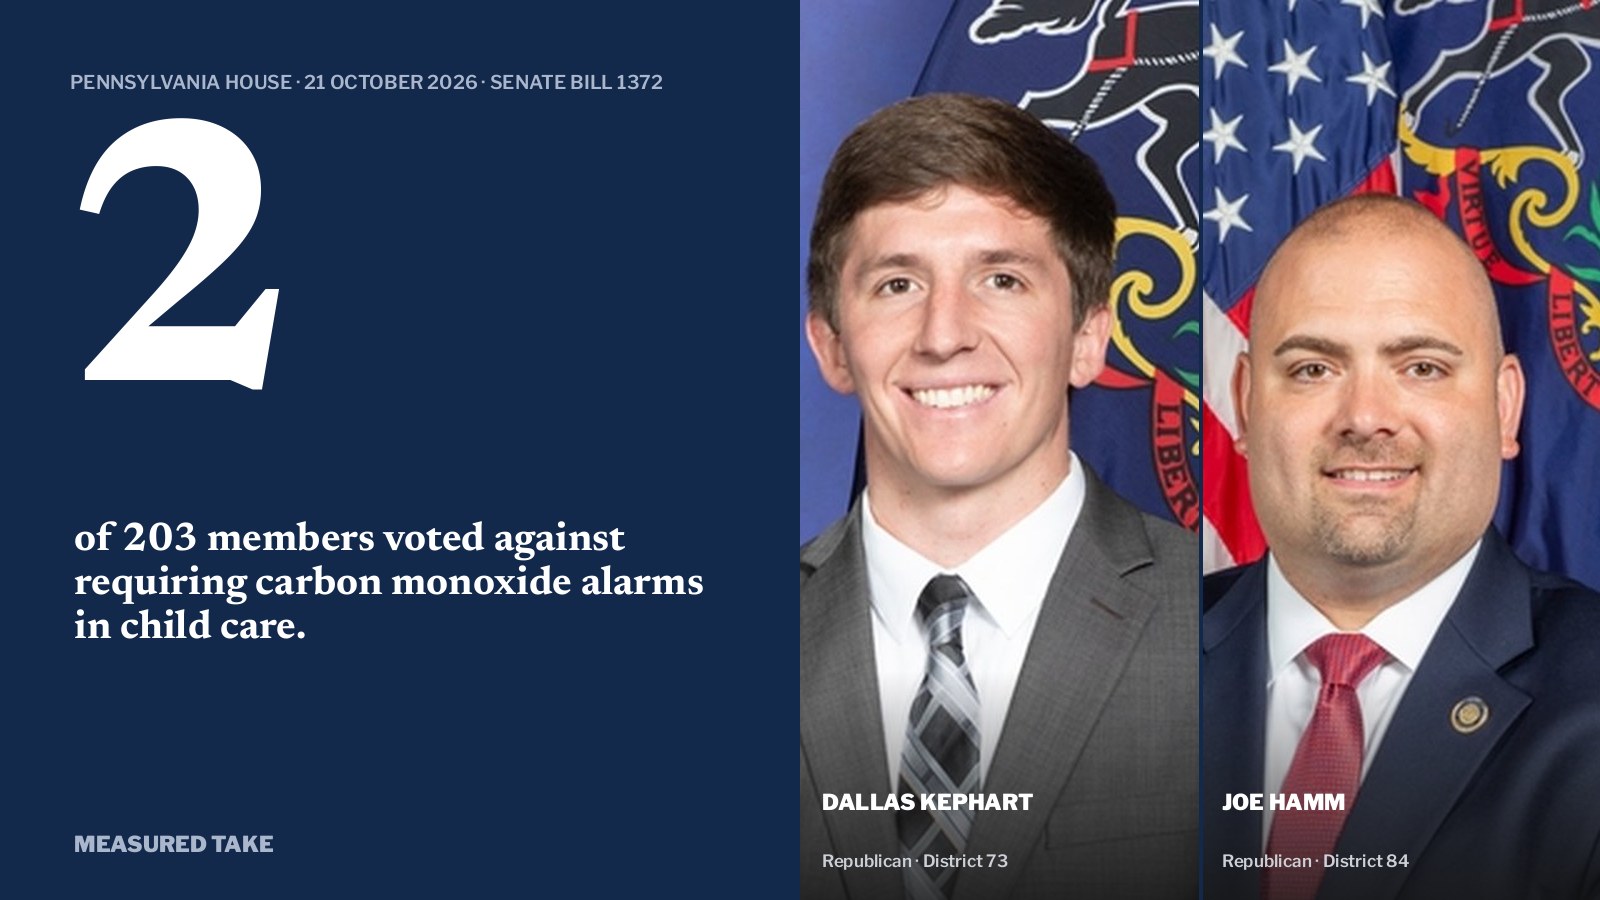
Pennsylvania House passes child care carbon monoxide alarm bill 201–2; Joe Hamm and Dallas Kephart vote no
Conversation
Reader notes
Loading comments...