Britain's 'Be Ready' Campaign: Three Days of Cash and Tinned Food as Cyber Resilience Policy
The UK government's three-year 'Be Ready' campaign asks households to stock three days of water, food and cash, signalling concern over payment and supply-ch...
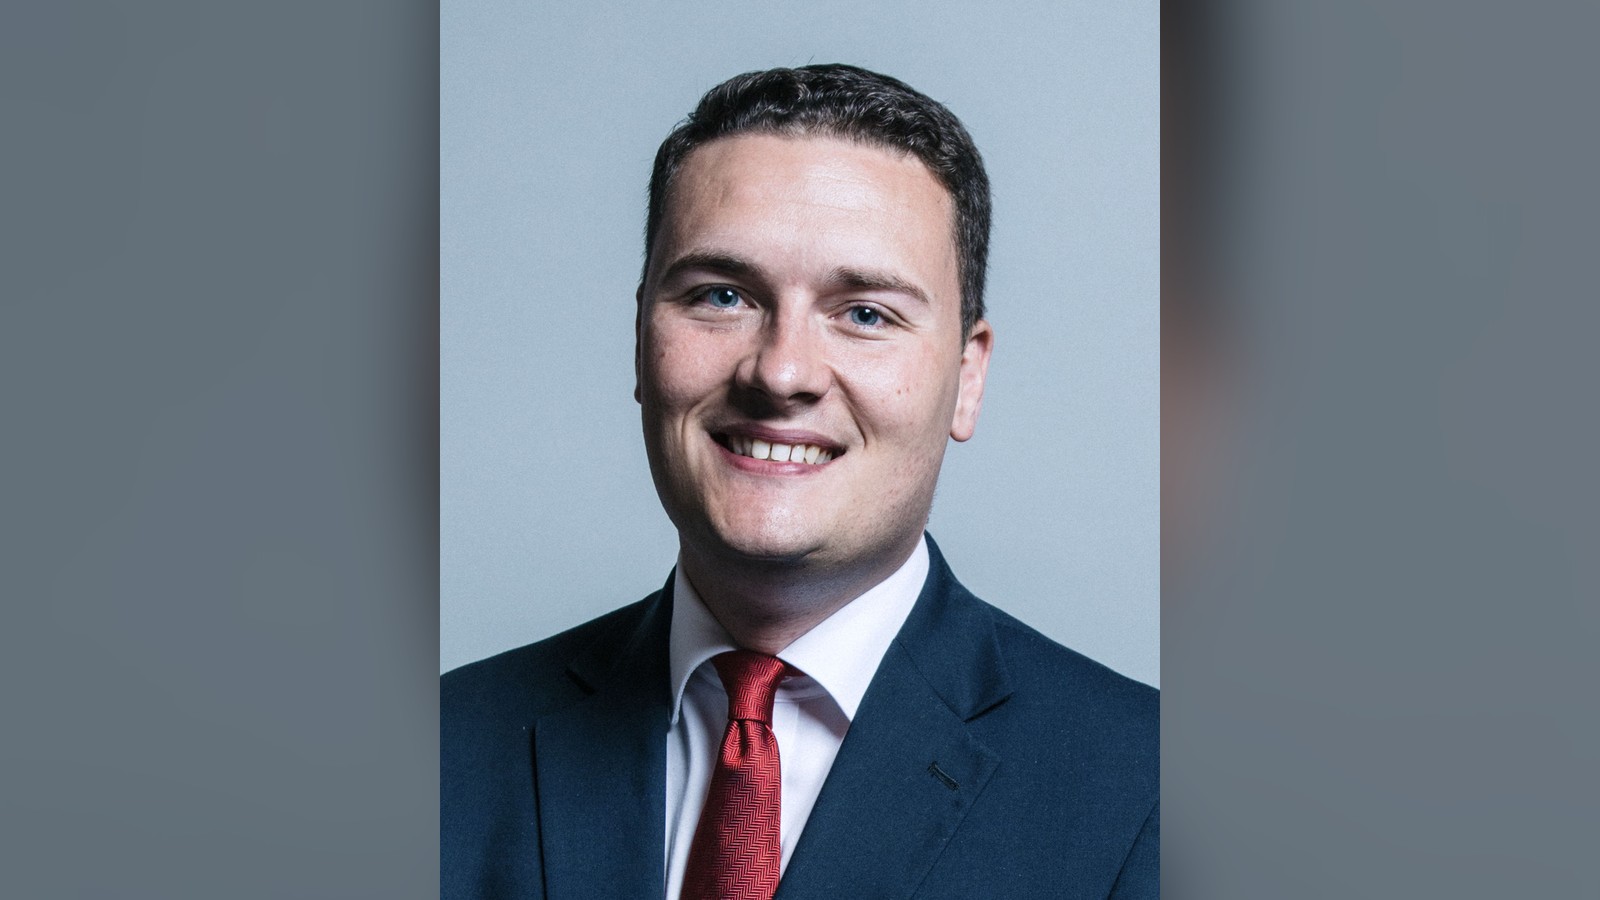
The UK government launched a three-year 'Be Ready' campaign on 22 October 2026, urging households across the country to prepare for emergencies and disruption. Defence Secretary Wes Streeting said businesses and individuals should be prepared for possible disruption to essential supply chains caused by 'hostile state actors or terrorists', and asked how people would cope if supermarket payment systems went down.
The guidance advises a minimum of three days' supplies: bottled water (up to nine litres per person), non-perishable or tinned food, a battery or wind-up FM radio, first aid kit, hand sanitiser, blankets, and cash in case electronic payments or ATMs are disrupted. A government study cited in coverage found only 13% of UK residents feel prepared for a major service blackout.
Streeting said he wanted people to be 'alert but not alarmed' and rejected accusations of scaremongering, adding that cyber incidents such as the critical security flaw in the PHP programming language will happen 'more and more'. Security minister Dan Jarvis said those who can follow the advice should do so. The campaign was discussed on BBC Question Time, where the audience laughed and some argued it was scaremongering.
The practical effect is a shift in responsibility. Continuity of everyday life — food, water, money — is now partly a household task, not solely an infrastructure guarantee. That signals official concern that cyberattacks or hostile-state action could interrupt payment systems and supply chains.
What Defenders Should Do
Sources
Editor & Founder
Peter OlaleruPeter is the founder and editor of Measured Take and a cybersecurity professional. He leads our news, fact checks, sport and guides from around the world, with a particular eye on cyber attacks, data breaches, scams, AI and misinformation.
More from Cybersecurity


Conversation
Reader notes
Loading comments...